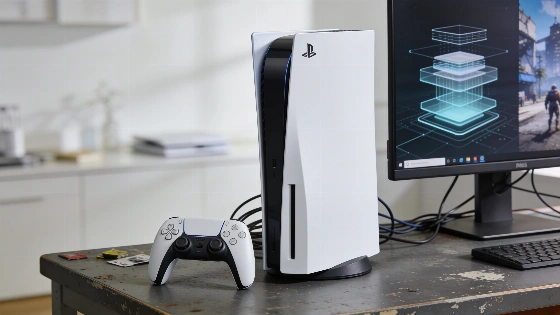
Byepervisor Reborn targets PS5 firmware 13.60 and 13.20, with 13.00 marked untested. It still needs an existing kernel-exploit chain and ships without a consumer-ready jailbreak package.
The flaw appears when a PS5 resumes from Rest Mode. During the S3 resume stage, the hypervisor calls the startup_mp hypercall on core 0 to initialize cores 1 to 15, temporarily applying an insecure Nested Page Tables configuration on those cores.
That brief opening is the basis of Byepervisor Reborn. The project, published by PS5Dev, can execute shellcode with read and write access to the hypervisor's address space, including its VM Control Blocks. According to the project's GitHub documentation, exploiting the flaw can also disable execute-only memory protections, leaving the kernel available to dump and patch.
A hypervisor sits below the console's operating system and helps control access to hardware and memory. Reaching that layer gives developers a deeper foundation for changing system behavior, but the exploit alone does not supply the separate tools needed to run homebrew applications.
Access without a jailbreak
The repository describes the release as a base for further development and warns that it is not useful to regular users in its current state. Its instructions require an existing kernel-exploit chain to load byepervisor.elf through elfldr. Byepervisor Reborn does not run independently on an ordinary PS5, and it includes no homebrew-enabling patches or complete consumer-facing jailbreak package.
That leaves developers with a new opening to work from, rather than a set of features PS5 owners can install today.
Firmware support is narrower
The initial implementation lists support for firmware 13.60 and 13.20. Firmware 13.00 is marked untested. PS5Dev describes the potential vulnerability range as 6.xx to 13.60, but that range does not confirm working support across those versions in this release.
The developers also suggest a modified implementation could work on firmware 14.00. They have not released it. The source notes that 14.00 has no public kernel exploit, so the current release does not establish a working route to a complete jailbreak on that firmware.
Console exploits depend on the specific system software and components available in each version. A vulnerability's possible reach does not establish that a tested, usable implementation exists.
Part of a faster-moving scene
Byepervisor Reborn arrives amid a busy period for PS5 hacking. In September, the Relapse exploit paired a browser vulnerability with kernel access. Its ELF loader brought publicly accessible exploitation to firmware 13.60. Relapse also improved on earlier methods that could leave a console hanging for around 50 minutes during an attempt.
Linux support has reached firmware 7.61. Existing homebrew includes emulators and unofficial 60 FPS modifications for older PS4 games. Native PS3 emulation has also emerged as a recent capability.
Separately, pLabs5's pLinux5-NG project describes a Linux boot effort for PS5 systems running firmware from 8.xx through 13.60. That project does not add Linux support to Byepervisor Reborn.
The PSBOX Cloud Gaming client brings Xbox Cloud Gaming to modified PS5 systems. It is another example of work developers are pursuing on homebrew hardware, not a feature included with Byepervisor Reborn.
Work still required
The exploit could lay groundwork for Linux support on newer firmware. Developers may also build improved homebrew for the platform. Neither outcome is a confirmed capability of the current release.
Updated payloads and patches still need to be produced. They must then be tested against the relevant firmware versions. The project's accompanying update describes continuing work to extend support to additional firmware.
An independent description by BiteYourConsole notes that the console may shut down if the resume-stage exploit fails.